While the term “agentic AI” has circulated in tech and business for some time, frontier AI companies like OpenAI and Meta are now reimagining it for the masses. Imagine an AI pet with a cute name and a distinctive personality that can perform tasks on your behalf. That’s essentially the idea behind OpenAI’s Dots and Meta’s Muse — personal AI agents designed to handle tasks for you.
The dream of “one cable to rule them all” is finally a reality, and dozens of devices are better off because of it. USB-C gave us permission to own fewer single-use cables than we used to, and it opened the door to interesting functionality that would otherwise be impossible, like running data, power, and video between a single port on a laptop and a monitor.
The customer data stolen from global fashion retailer ASOS includes more than just names and contact details, raising questions about its early reassurances.
As we reported earlier this week, ASOS customers received a push notification through the ASOS app alleging that the company had been hacked.
ASOS has confirmed that attackers accessed customer information after tricking an employee into handing over login credentials. While the retailer says payment card information and customer passwords were not accessed, reporting by the BBC shows the stolen information includes more than the “basic personal information” initially mentioned by the company.
The stolen login details were used to access information on third-party platforms used by ASOS. The company says it locked down the affected platforms and launched an investigation with internal and external specialists. It also says it has strengthened its security controls.
What data was stolen?
In our initial coverage, we highlighted the potentially detailed customer profiles associated with ASOS’s marketing setup. The BBC’s findings now establish that at least some shopping-related information was taken.
According to the BBC, which received a sample from the attackers, the exposed data includes:
Names and home addresses
Phone numbers and email addresses
Customer numbers and dates of birth
Searches customers made on the ASOS website
Details such as when a customer started using ASOS
The BBC reported search terms including “reclaimed vintage,” “glamorous wide fit,” and “Asos petite.” That makes this more than a stolen contact list. The information can also reveal customers’ shopping interests and their relationship with the retailer.
The attackers’ original notification named Snowflake, a data storage and analysis platform. They subsequently told the BBC that they accessed the information through Simon AI, a platform built on Snowflake that ASOS uses for customer personalization.
Snowflake said it had found no compromise of its platform. Using stolen credentials to access a customer’s account or a connected service does not necessarily mean the underlying platform was breached. The available reporting does not establish a vulnerability in Snowflake or Simon AI.
ASOS’s communication with customers
Customers first heard about the breach from the cybercriminals, rather than the retailer. The attackers’ decision to send a notification through the ASOS app may have made that unavoidable.
But the Independent reported that ASOS’s full statement followed roughly five hours of silence, leaving customers alarmed by the notification and waiting for an explanation.
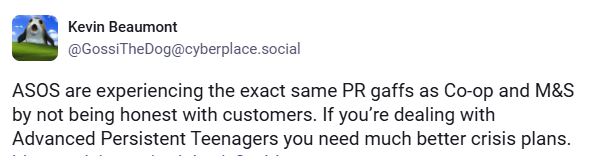
Security expert Kevin Beaumont criticized the response:
“ASOS are experiencing the exact same PR gaffs as Co-op and M&S by not being honest with customers. If you’re dealing with Advanced Persistent Teenagers you need much better crisis plans.”
While the attackers are threatening to release the data, ASOS says its full investigation will continue over the coming weeks. It will contact customers directly where it believes further information, support, or action is required.
Reportedly, the group gave ASOS two weeks to make contact and said it wanted a ransom in exchange for deleting customer information. ASOS did not disclose whether it would pay.
How to stay safe
ASOS says its website and app remain safe to use, and that payment card information and customer passwords were not accessed. But the stolen details and shopping searches could help scammers make targeted phishing messages more convincing.
A message that knows your name, or what you searched for, isn’t proof it came from ASOS.
Be wary of unexpected emails, texts, or calls about the breach, refunds, deliveries, or problems with your ASOS account.
Don’t follow links in unexpected messages, and don’t follow the Telegram link in the attackers’ message or engage with them. Go directly to the ASOS website or app to check your account.
Don’t share passwords, security codes, or payment details in response to an unsolicited message or call. ASOS says it will never ask you to do this.
Your name, address, and phone number may already be for sale.
Data brokers collect and sell your personal details to anyone willing to pay. Malwarebytes Personal Data Remover finds them and gets your information removed, then keeps watch so it stays that way.
The community often recommends self-hosted apps like Pi-hole, Vaultwarden, Audiobookshelf, and more. These aren’t the only options; plenty of other self-hosted tools can do truly ingenious things. Many of them are lightweight enough to run on that old Raspberry Pi you should still have in your drawer.
Halloween is almost upon us again, and for those of us blessed with one (or more) 3D printers, it’s the perfect time to get into the real spirit of Halloween and decorate your home with things you can’t just buy off store shelves.
Microsoft announced that it will add .msix and .msixbundle attachments to the list of blocked attachments in Outlook Web and the new Outlook Windows client starting next month. […]
Smart locks can be wonderful — until you’re locked out of your home when the battery dies. Amazon’s Ring believes it has a solution with a new Ring Smart Lock that you can recharge with a crank.
If you’re a middle-aged geek like me, you’ll love a good hobby. Whether you’re obsessed with pulling the perfect god shot of espresso or building the perfect audiophile setup, a lot of hobbies can get very expensive. They don’t have to start that way; plenty of great tech hobbies let you start with gadgets you may already have lying around.
Hackers are exploiting stored cross-site scripting (XSS) vulnerabilities in two unrelated WordPress plugins, Ninja Forms and WPC Product Bundles for WooCommerce, to install backdoors and create rogue admin accounts. […]