Samsung has a reputation for packing its Galaxy phones with a deluge of features, arguably more than any other Android phone maker, and many of them don’t get the spotlight they deserve. As a result, a lot of people overlook a good chunk of their Samsung phone’s features just because they aren’t talked about, which is a shame because some of them can be super useful in a variety of situations. Here are five One UI features that most owners end up ignoring, but if you own a Galaxy phone, you really shouldn’t.
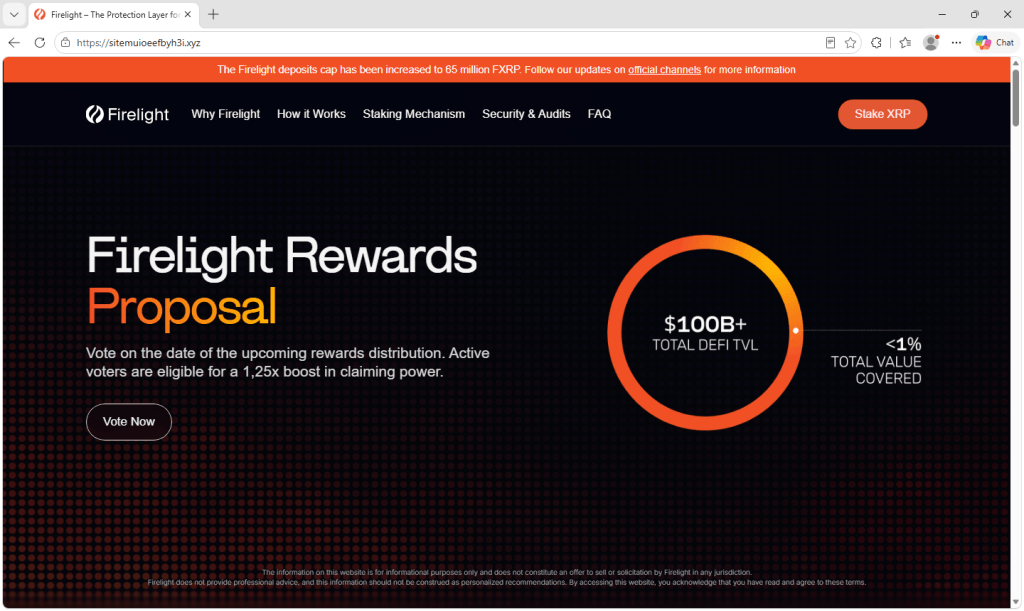
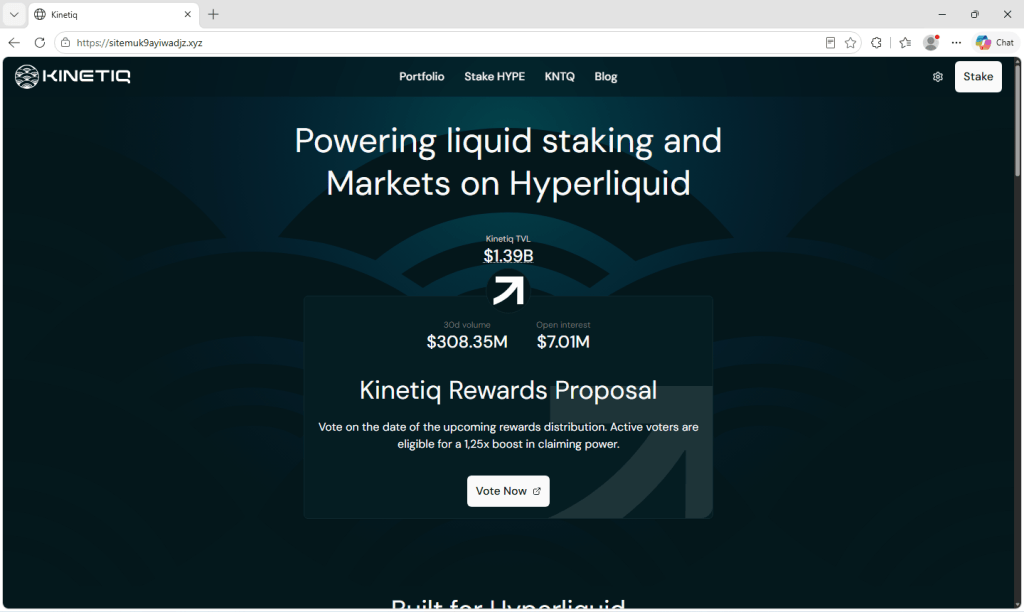
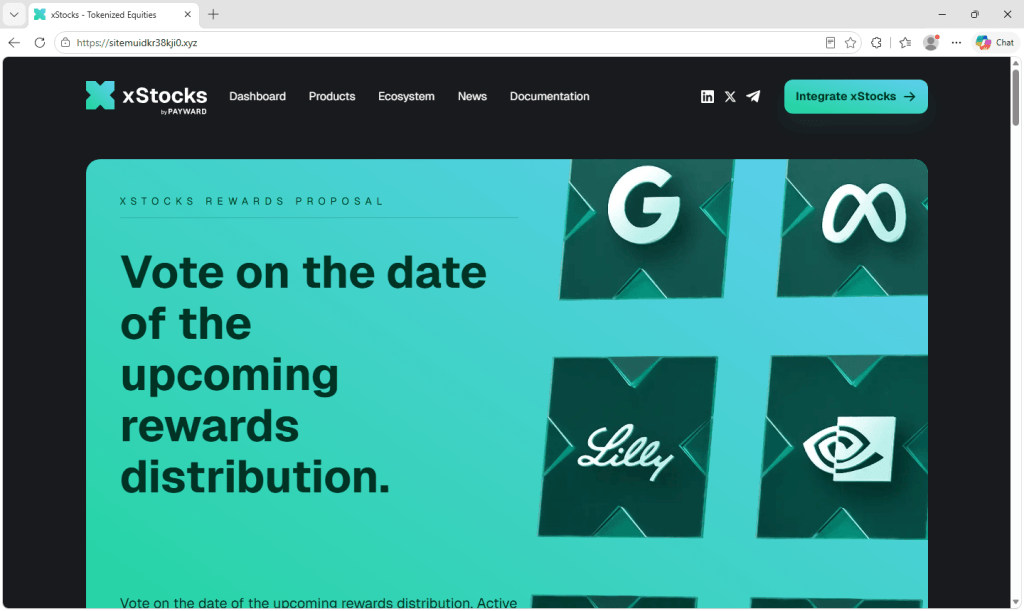
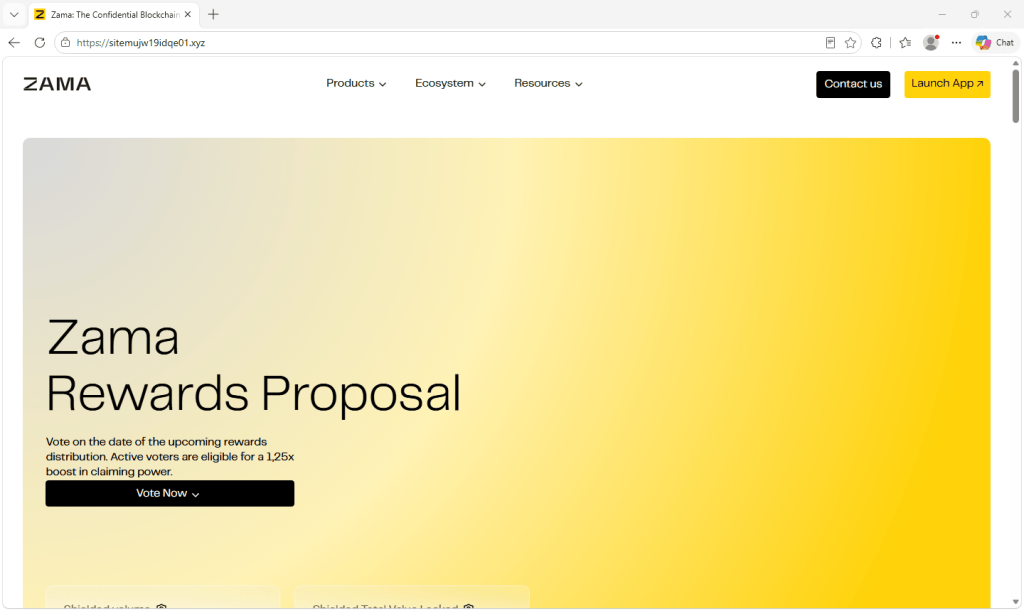
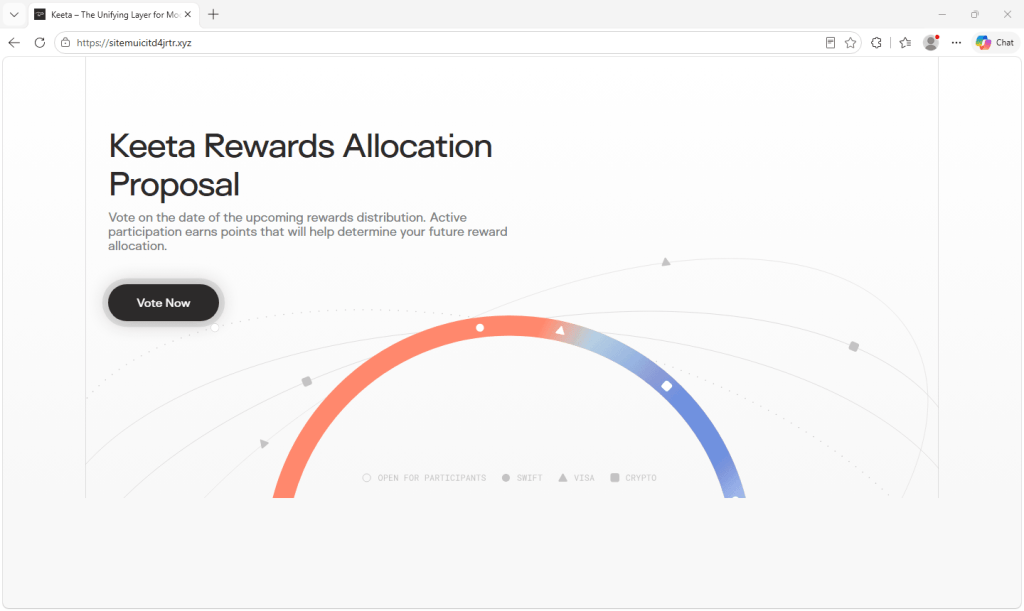
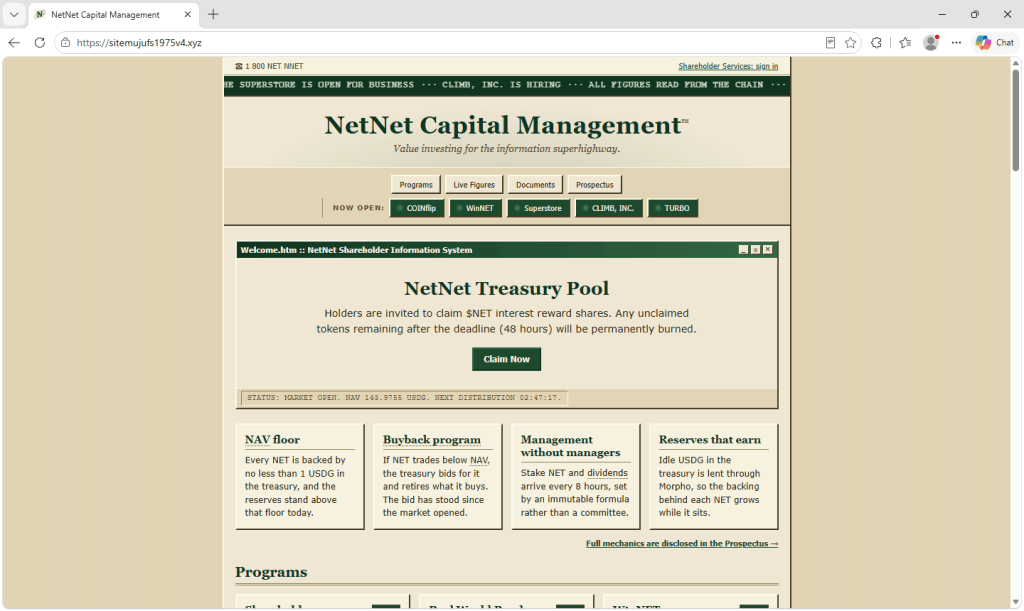
We found 70 websites that impersonate legitimate crypto projects that invite visitors to vote on the date of an upcoming rewards distribution.
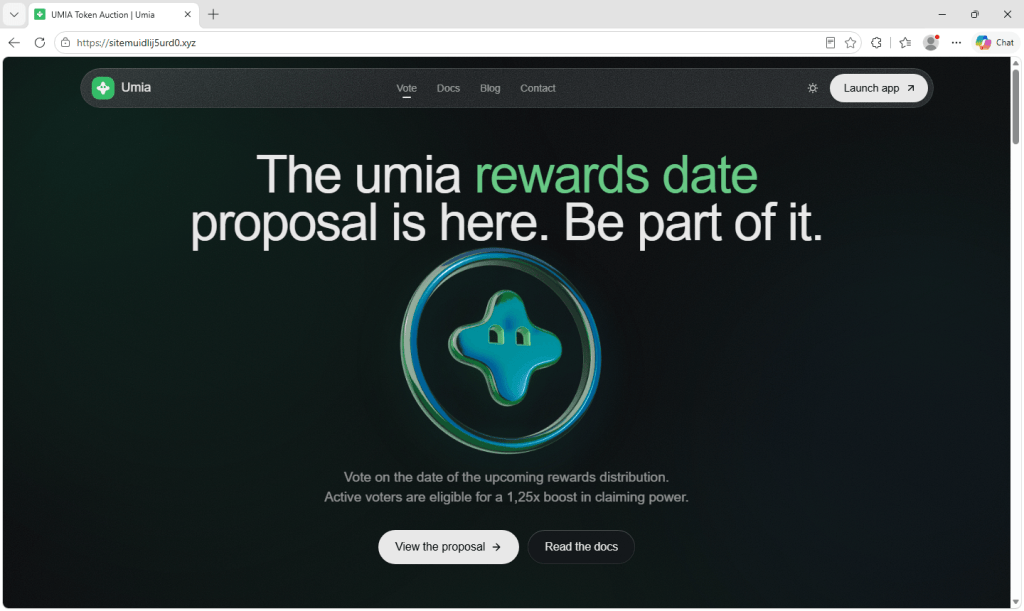
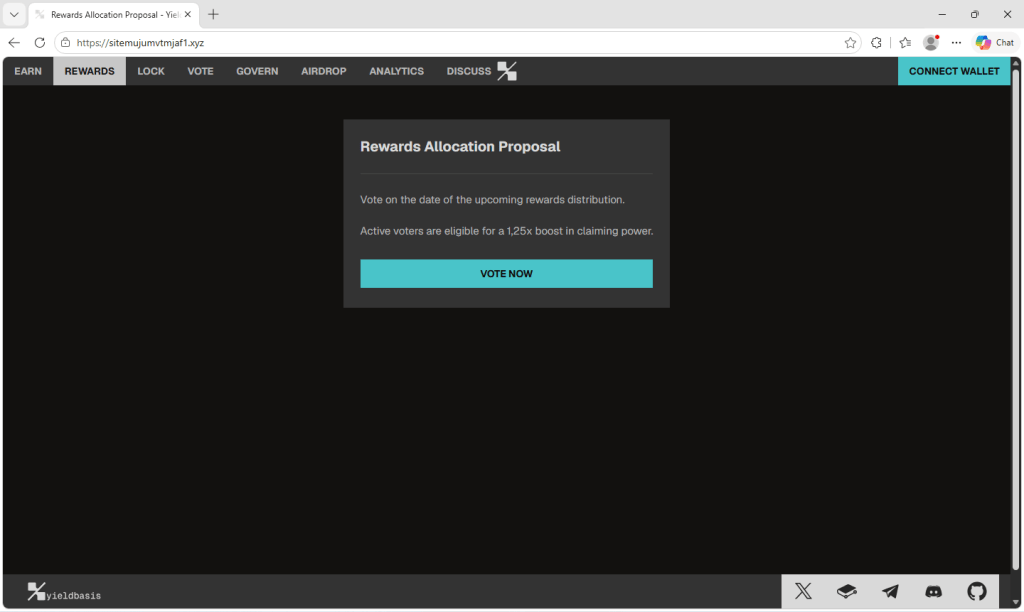
The pages copy the look of the real sites closely, and on most of them the offer is small and believable: Cast a vote, and as an active voter you get a 1.25x boost when the rewards are paid out.
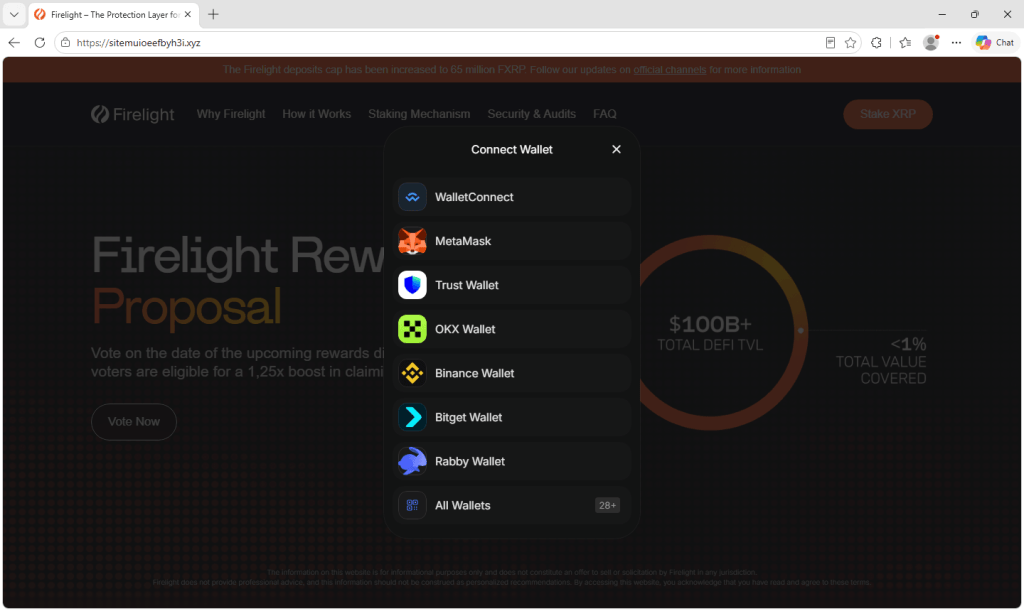
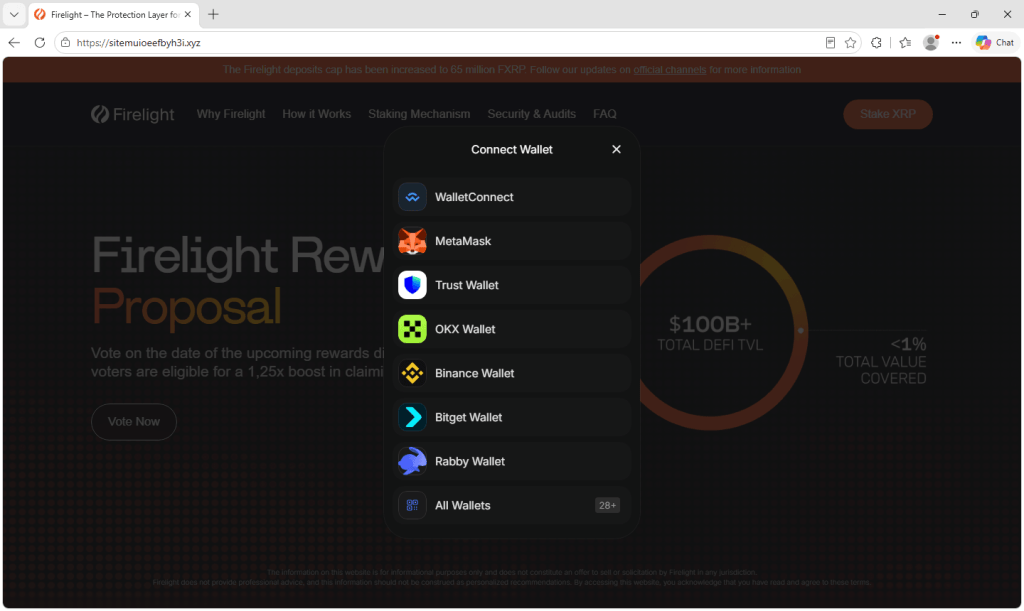
However, the vote is fake and clicking the Vote now button opens a wallet connection prompt. It’s the first step toward requests that could trick visitors into authorizing access to their tokens.
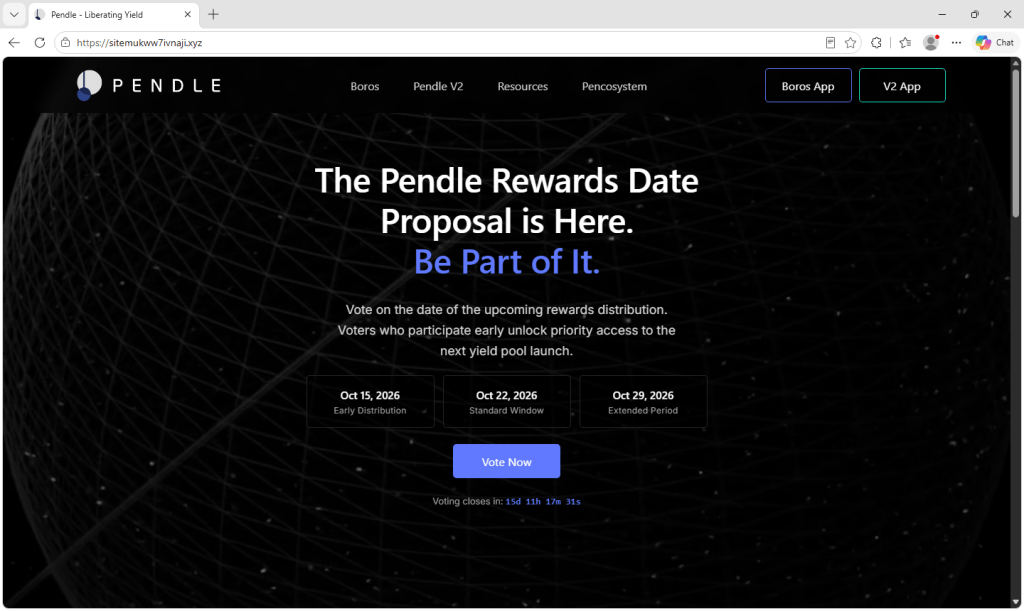
The brands being copied include xStocks from Kraken, Pendle, Zama, Kinetiq, Yield Basis, Firelight, and smaller platforms including Umia, Keeta, and NetNet. None of these pages are affiliated with the projects they imitate.
Copies of familiar brands
Each site is a close copy of the project it targets, down to the logo, menus, and colors. The Firelight copy even carries a real announcement about the protocol’s deposit cap, suggesting the pages were copied from the live sites rather than rebuilt from scratch.
Most use the same wording about voting on the rewards date to earn a boost, though a few vary the pitch. The Pendle copy adds fake dates and a countdown to create urgency, the Keeta copy promises points instead of a boost, and the NetNet copy skips the vote and warns that unclaimed tokens will be burned after 48 hours.
Why these brands
The choice of targets does not appear to be random. Several of the impersonated projects have held a token launch, airdrop, or public token sale within the past year. Others run points or rewards programs. Their communities are used to hearing about rewards, claims, and allocations, and are primed to act on them.
Zama ran a public token auction in January, and its token began trading in February. Kinetiq launched its governance token alongside an airdrop to early users in November 2025. Umia’s token auction ran from August 29 to September 2, only weeks ago. Firelight awards points to early depositors, and Pendle launched on Robinhood Chain on September 4.
A message about rewards from one of these projects would not sound strange to someone who follows it. The lure appears designed to appeal to people who already hold the token or have used the protocol, because they’re the ones who might expect a distribution and want a bigger share.
What happens when you click vote
The Vote button does not lead to a ballot. It opens a Connect Wallet window that is the same regardless of which brand the page imitates. It lists WalletConnect, MetaMask, Trust Wallet, OKX Wallet, Binance Wallet, Bitget Wallet, and Rabby, along with an option to browse more than 28 others.
This window resembles the connection prompts people see on legitimate crypto sites, which may make the request seem routine.
Connecting a wallet on its own shares the wallet’s address, allowing the site to look up its holdings. At this point, it does not give the site permission to spend your tokens.
The damage typically comes from what the site asks for next. In wallet-draining scams, a page may follow the connection with a request to sign a message or approve a transaction, presented as confirming the action the visitor came to take. A malicious approval or signature can give the attacker permission to move tokens out of the wallet without further confirmation.
Blockchain transactions generally cannot be reversed, so stolen funds are very difficult to recover.
Signs of a single operation
Several details suggest a shared operation or phishing kit. All of the domains listed at the end of this article follow the same pattern: sitemu followed by a string of apparently random characters, on the .xyz top-level domain.
The same templates are reused across several different brands, with the text appearing almost word for word whether the page is dressed up as Zama, Firelight, or Yield Basis—right down to writing the boost as 1,25x, with a comma in place of the decimal point. The wallet connection window behind the Vote button is identical across the brands as well.
Random domain names spare the operator the work of coming up with a convincing lookalike address for each brand, and losing any single site costs them little. They also make the address bar one of the clearest giveaways on these pages.
How to protect your wallet
Check any claimed vote or rewards distribution through the project’s official channels before connecting your wallet. A familiar logo is easy to copy.
Check the address, not the design. These pages closely copy the real thing, so branding alone cannot establish that they are genuine. If the domain is not the one the project officially uses, close the tab.
Go to the project directly. If a vote or a reward is genuine, it will be on the project’s official site or announced on its established social accounts. Use a bookmark or type the address yourself rather than following a link from a message, ad, or reply.
Read what your wallet asks you to sign. Voting should not require you to approve spending of your tokens. If a signature or transaction request mentions approvals, permits, or transfers, reject it. Wallets that preview the outcome of a transaction can help, but do not approve a request you cannot understand.
Be wary of boosts, bonuses, and deadlines. Promises of extra rewards and warnings that unclaimed tokens will be burned can pressure you to act before checking.
Keep most of your funds in a separate wallet. Use a wallet with a small balance for unfamiliar sites, and keep long-term holdings in a wallet that you don’t use for those connections.
If you already connected, disconnect from the site. If you also signed a message or approved a transaction, use your wallet’s approval-management feature or a trusted token approval checker to review and revoke suspicious permissions. Disconnecting alone does not revoke token approvals. If you suspect your recovery phrase or private key was exposed, move remaining funds to a new wallet created with a new recovery phrase.
How Malwarebytes helps
Malwarebytes Browser Guard can block known phishing and scam sites before you interact with them. That is useful in campaigns like this one, where the fake page closely resembles the real thing.
If you receive a link to a rewards vote, claim page, or airdrop and are unsure about it, Malwarebytes Scam Guard can help assess the link before you connect your wallet. Check the offer through the project’s official channels too.
The Galaxy S26 line might be half a year old, but its official price is going up. Samsung has raised prices across the core series by at least $100, with steeper increases at the high end.
“Arizona’s court system was targeted by a cyber attack from criminal hackers or their bots.”
This is how the Arizona Supreme Court announced that hackers had attacked the state’s court system and stolen the personal information of “many Arizonans.”
The court says the attack began with a phishing email containing a malicious link that a court employee clicked. The attackers copied sensitive backup files containing records related to protective orders and foster care cases.
The court says it has no evidence, so far, that information about jurors, witnesses, or court employees was included in the copied files. It has not identified the attackers or a motive. It says the case is under investigation with the FBI, and no ransomware group has publicly claimed responsibility.
In an update, the court revealed that the attackers copied more than 150,000 recommendation reports created by Arizona’s Foster Care Review Board. The reports cover current and past cases involving children’s care and protection, dating back to 2010.
Those documents can include information about children, names of involved parties, case materials considered by the board, findings, and recommendations for courts, parents, and the Arizona Department of Child Safety. The court says the reports do not contain contact information such as addresses or telephone numbers.
The copied files were backups stored in a highly compressed format, kept for recovery after ransomware and other destructive incidents.
Information associated with protective orders can raise particularly serious safety and privacy concerns. These orders can protect people from abuse, harassment, or threats. Even where some records are public, combining names, case details, locations, and other sensitive context could create risks for people who are trying to limit their exposure to an abusive or threatening individual.
Breaches happen every day. Don’t be the last to know.
The court currently says it has no evidence that the information has been shared. As with many breach investigations, however, this can change as investigators determine exactly what was taken and monitor for publication, sale, or misuse of the data.
Arizona has about 8,000 children currently in foster care, according to the court. It is contacting people believed to have been affected.
What to do if you’re affected
Check the court’s advice. Every breach is different, so check its dedicated webpage for updates and follow any specific advice it offers.
Watch out for impersonators. Cybercriminals may contact you posing as the Arizona Supreme Court, another government agency, or someone you know. Verify anyone who contacts you through a separate, trusted channel.
Take your time. Phishing attacks often impersonate people or brands you know and pressure you to act urgently, using themes such as missed deliveries, account suspensions, and security alerts.
Get an early warning if your information appears on the dark web. If you’ve been notified that your information was copied in the Arizona court breach, identity monitoring can help you watch for signs of exposure and get support if you become a victim of identity theft.
Let’s face it, an incognito window can only do so much.
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance.
There are a few things you should double-check before turning a laptop into a NAS. While you definitely can just do it, these three BIOS options are definitely worth double-checking before diving down the rabbit hole.
Changing your DNS server is one of those simple networking tweaks that can make browsing safer, but DNS privacy is easy to misunderstand. Changing your DNS provider does not make your browsing history invisible. Your ISP, employer, school, or network administrator may still have other ways to determine which services you are connecting to.
The Dutch Institute for Vulnerability Disclosure (DIVD) suffered an AI-driven cyberattack that the organization described as “loud and very, very messy.” […]
Many DIYers start with one brand of power tools, then eventually switch things up. Like initially buying Milwaukee or DeWALT, then moving to Ryobi’s more affordable line. A common solution to having a mix of different tools, battery packs, and chargers is to buy a battery adapter. And while some people use adapters just fine, you probably shouldn’t use them on your Milwaukee battery packs, and here’s why.